to install the program or save file to disk to copy it to your hard drive.
Contents
NT4 128-bit Encryption Service Pack 5Netbus 1.60 Netbus 1.60, Get currently logged in user rights remotely. (525K)
TCPVIEW TCP Viewer by Dr. Mark Russinovich. Sort of a GUI netstat. Know who's connected to your box. (Connected AND unconnected endpoints). Works very well under NT, although it lacks auto-refresh. Small footprint. (36K)
Sechole3 Get admin access on NT with only read/execute on the local box or console. NOTE: Doesn't work with SP4 (56K)
NT Admin Boot Disk Linux Boot Diskette for NTFS, resets the Administrator Password. Use rawrite.exe (included) to make the floppy from the .bin file NOTE: May not work with SYSKEY. (1.4M) NEW! Updated .bin file located here:
Netbus 1.70 Netbus 1.70, Latest version similar to 1.60 above. (549K)
NetBuster This version removes all trojan versions of Netbus. Also will simulate the server portion of Netbus allowing you to "put the fear" into whomever is trying to Netbus you.(546K)
NetLab For NT/95 An excellent combination program with Finger, Trace, Quote, WhoIs, Port scanner, other neat goodies.(467K)
InControl4 Run this before installing ANYTHING questionable. Takes a snapshot of the entire registry, drive contents. Tells you nearly every change a piece of software makes to your system. (823K)
HotFix Control Tells you what hotfixes and service pack you have applied, neat utility. (163K)
Netbus Pro 2.10 (Final Release, not the Beta) The first of the Non-Trojan Netbus. This version can actually be considered a legitimate program this time. (1.8 M)
User2SID/SID2User Look up the SID of any domain account. Want to know what SID belongs to what user account? (50k)
PrcView Process viewer This one is a "Must Have" utility written by Igor Nys of Computer Technology Inc. View all active processes on your NT or95/98 box as well as their .dll dependencies. Do you know that you've been "NetBussed" but you don't know the name of the .exe? Click on "View/Module Usage" for a list of the all modules in the system alphabetically sorted, highlight the "keyhook.dll" and PrcView will show you the module(s) that use this dll. Bingo! You've found your trojan. (77K)
Forensic Toolkit for NT A collection of VERY useful NT command line utilities from NT OBJECTives Inc. that allow you examine the files on a disk drive for unauthorized activity. Click here to view the "readme.txt".
NTLast Version 1.6 Another useful one from NT OBJECTives that searches the Event Log for Interactive/Remote/Failed logon stats. It distinguishes between remote/interactive logons and matches logoff times with logon times.
NTO Scanner Version 1.26 Hands down one of the quickest NT TCP/IP Port scanners, scans all 65,000+ ports in under 8 minutes. Click here for more details.
NTO "Seek and Destroy" Tools Four new tools from NTObjectives, that include:
NTOLog™ - Powerful, network wide backup/clear utility for NT logs
LServers™ - NetBIOS name dumper
NPList™ - NT network process dumper
NTODrv™ - NT network driver/service dumper
NTO's PacketX Native Windows NT firewall testing tool that allows for complete TCP/IP packet creation. Click here for more info.
DelGuest- From Arne Vidstrom of Ntsecurity.nu. DelGuest deletes the built-in Guest account in Windows NT. This account is supposed to be impossible to delete, and it is impossible to delete through the ordinary user interface, but with DelGuest you can do it. More information can be found in the DelGuest FAQ
Inzider - Another one from Arne at NTSecurity.nu. This is a very useful tool which lists the current processes in your Windows system and the ports each one listen on. It is written to work on Windows NT and Windows 9x, and I know of no other program which does what inzider does. There have been some stability problems on Windows 9x, which I thought were solved but were still left although not as frequent. In the new version (1.2) I have done a few changes to improve both stability and reliability. I guess there is still much left to wish for, but over all I think inzider is a success, and it's quite popular despite the problems. On Windows NT, inzider is still unable to check processes which are started as services. Yet, it's very useful - for example, check out this page about inzider vs. bo2k (Back Orifice 2000). Keep your eyes open in the future, there will most likely come new improved versions. Here is a handy link to the FAQ.
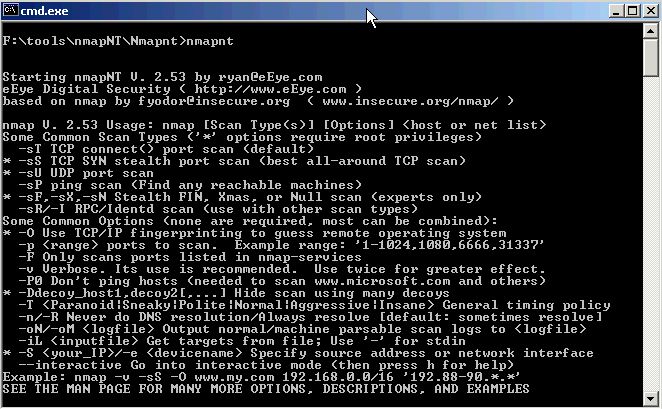
NMapNT - "If your goal is to understand your network from a 40,000-foot view, then Windows port scanning tools will suffice. But if you're serious about your security and looking for the holes that crackers will find, then take the time to install a Linux box and use nmap." -- Info World Well, someone FINALLY did it! NMAP is now ported for Windows NT. eEye Digital Security's NMAP ported for NT (Also tested by us under Windows 2000 Advanced Server) complete with source code. For more info on eEye, see their website or our very own "Top Drawer Picks" Here's a screen shot with valid arguments listed:
Cerberus Information Scanner - An
excellent portable IDS scanner, designed by David Litchfield (You may
know him as Mnemonix) of Cerberus Information Security. It was designed with
three things in mind:
- Find known vulnerabilities
- Ease of use (It's Command Prompt based)
- Portability (It's size is only 110k)
XTeq's X-Setup 5.5 - Called "The Mother of All Windows Tweak Programs", this program lends a handy way to personalize your system. Edit boot options, stop programs from automatically loading with Windows, and remove items from the uninstall list. It also contains some handy security settings and administrative options, normally done by editing the registry. Visit their site for more details and add-ons.
Resplendent Resolver For NT/2000 - Don't you just hate it when you try to install or run a program and it whines about "Requires Windows NT SP3", even though you're running SP5 or Windows 2000? Try out this little gem from from Resplendence. More Info...
Panda AntiVirus Command Line A little clunky, but still catches all those nasty little Virii and trojans, INCLUDING BO2K. Best of all, it's FREE!
Syntax: PAVCL [Parameter] [What to scan] [Parameter]
Possible parameters:
/NOM Do not scan
memory.
/MEM Scan memory even if there is no file to scan.
/NOB Do
not scan the boot system.
/NOF Do not scan files.
/ALL Scan all
drives in the computer system.
/LOC Scans local drives.
/ITW In the
wild.
/NBR Does not allow interrupting the program with ESC or
Ctrl-Break
/INVA Investigate drive 'A' for unknown viruses.
/INVB
Investigate drive 'B' for unknown viruses.
/CLV Remove the viruses
found.
/LIS List of viruses known to this version.
/SAV Saves the
parameters to a file. The next time it is run, they will be added to the
ones specified for that session.
/NSB Do not scan nested
subdirectories.
/PTH Scan the directories specified in the DOS PATH
environment var.
/ISO Activate isolation mode.
/HEU Activate
heuristic detection method (and lastly) /CMP Search for viruses into
compressed files. (ZIP, ARJ, LZEXE)
List of Well Known Port Numbers Well Known Port Numbers. (49K)
Bo Freeze Detects subnet scans by remote hosts looking for Bo Servers,
logs the scans, and then sends malformed packets to the remote host
running the BO GUI causing the remote BO GUI to freeze or lock up. (73K)
telnet_nb Test for NetBus. This only checks the default port.
It is still a good idea to run a Virus Scan and also check your system's registry.
If your program answered with "Netbus 1.xx" you are definitely affected.
Notice how I said "affected" instead of "infected". These are trojan programs, not trojan Virii
(although unknowing people can spread it like Virii).(1K)
Alpha Taskbar Wallpaper Version 3.0 Customize the background of your taskbar. (788K)
Hacker 1.0 Hide or disable a window, change a window's title, icon, font and background. (546K)
LANChatPro User-friendly Local Area Network chat for Win 95/98/NT. (443K)
LANChat-1.0.2.tar.gz Linux Console version, third release, compatible with LANChat for Windows.
XLC10b-bin.tar.gz First Xwindow version, compatible with LANChat for Windows.
. (K)
. (K)